
SYDNEY · PRIVACY, DATA & AI GOVERNANCE
Privacy, Data & AI lawyers for Sydney business owners
Practical advice on privacy, data protection and AI governance to keep your business compliant, secure and moving.
- Fixed fees. No surprises.
- Clear advice, practical solutions.
- Sydney-based, serving clients Australia-wide.
- Senior-led. Commercially minded.


25+
Years of commercial experience
1 firm
Clients Australia-wide
100%
Senior lawyer-led
15-min
Obligation-free initial call
Overview
Privacy and AI advice for businesses
Most data and AI decisions have legal consequences
We advise on privacy compliance, data practices, AI use and technology systems that shape how your business collects, uses, stores and shares information.
You deal with one lawyer who understands your business and can support the matter from the first conversation through to resolution.
Watch · 46 sec
How we help businesses move forward
What we do
How we help you handle data & AI
A senior lawyer handles your matter with cross-disciplinary expertise, from the first conversation through to resolution.
01
Privacy policy & website terms
We draft privacy policies, cookie notices and website terms for your business.
View
02
Workplace AI policy & governance
We help employers set clear rules for staff AI tool use.
View
03
Direct marketing & digital tracking
We advise on direct marketing, tracking tools and Spam Act compliance.
View
04
Data mapping & PIAs
We map your data and carry out privacy impact assessments.
View
05
SME privacy compliance audits
We review your privacy practices to identify real compliance gaps.
View
06
Data breach & NDB response
We advise on data breaches and notifiable data breach obligations.
View
07
DPAs & cross-border transfers
We manage data processing arrangements and cross-border disclosures.
View
08
Data retention & destruction
We advise on retaining and securely destroying personal information.
09
Access & correction requests
We help businesses respond to access and correction requests.
Ready to talk it through?
We’ll discuss your matter. There’s no pressure to proceed.
Who we act for
Business owners, founders & executives
SMEs across professional services, health, construction, hospitality, retail and creative industries.
SME owners & founders
Managing customer and employee information as the business grows.
Employers & senior managers
Handling staff data, workplace monitoring and privacy risk.
HR and people & culture leads
Managing employee records and recruitment systems.
Operations & compliance managers
Overseeing data handling, vendor contracts and privacy audits.
In-house business advisers
Managing privacy obligations and emerging AI risks.
Growing & multi-site businesses
Building data governance as systems and locations expand.
What our clients say
- Updated privacy policy
- Website collection notice
- Cookie notice
- Automated decision-making check
BEFORE 10 DECEMBER 2026
Is your privacy policy telling the truth?
New privacy policy rules for automated decision-making start on 10 December 2026. Our fixed-fee Truth Check reviews your policy against how your business actually operates, for $1,290 + GST.
Engagements confirmed by 10 December 2026 include the automated decision-making check.
Ready to talk it through?
We’ll discuss your matter. There’s no pressure to proceed.
Why Connected Legal + Commercial
Why work with us?
One lawyer, the whole picture
Work with one lawyer who understands your business and data systems.
Commercial judgment, not just legal opinion
We understand privacy pressures firsthand and give clear, practical advice for considered decisions.
Plain English, always
No jargon, no long letters restating the law. You’ll understand where you stand and what happens next.
Fixed fees. No surprises
Scope and cost are set out upfront, so there’s no anxiety about what a phone call will cost.
Prompt response
Time-sensitive privacy matters get a prompt response when you need it.
Our process
Four steps, no surprises
From first enquiry to completion, you’ll always know where you stand and what happens next.
01
Understand your data systems
We review how your business collects, uses and shares information, and the technology involved.
02
Risk Assessment
We explain where your current approach may fall short, what the law requires and recommend solutions for your business.
03
Set the scope & next steps
We confirm the action plan, costs and timeline with you before proceeding.
04
Implementation
We help you put the agreed changes into practice and keep you updated until resolution.
Key things to know
Key things to know about privacy, data & AI governance
An introduction to the legal issues that affect SME data and AI use.
01 Notifiable data breaches
If personal information is lost or accessed without authorisation, your business may need to notify affected individuals and the regulator. The rules apply regardless of business size.
Many businesses only discover this obligation during a breach, when timeframes are already running. We help clients understand their notification duties before an incident occurs.
02 AI tools & automated decisions
Many everyday tools use AI to make decisions that affect real people. Your business may need to notify and disclose this kind of automated decision-making in their privacy policy.
Most businesses don’t realise their existing tools may already trigger this obligation. We help clients identify which AI tools need disclosure and update their privacy policy to meet it.
03 Privacy policies vs actual practice
A privacy policy only protects your business if it reflects what actually happens with customer and employee data day to day.
Policies drift out of date as systems change. We help businesses check that their policy matches their real data practices, not just what was true when it was written.
04 Third-party & vendor data sharing
Sharing personal information with software providers, contractors or platforms can trigger obligations, even when your business doesn’t directly control that data.
Vendor terms are often accepted without a privacy review. We help businesses check what their key providers actually do with the data they’re given.
Ready to talk it through?
We’ll discuss your matter. There’s no pressure to proceed.
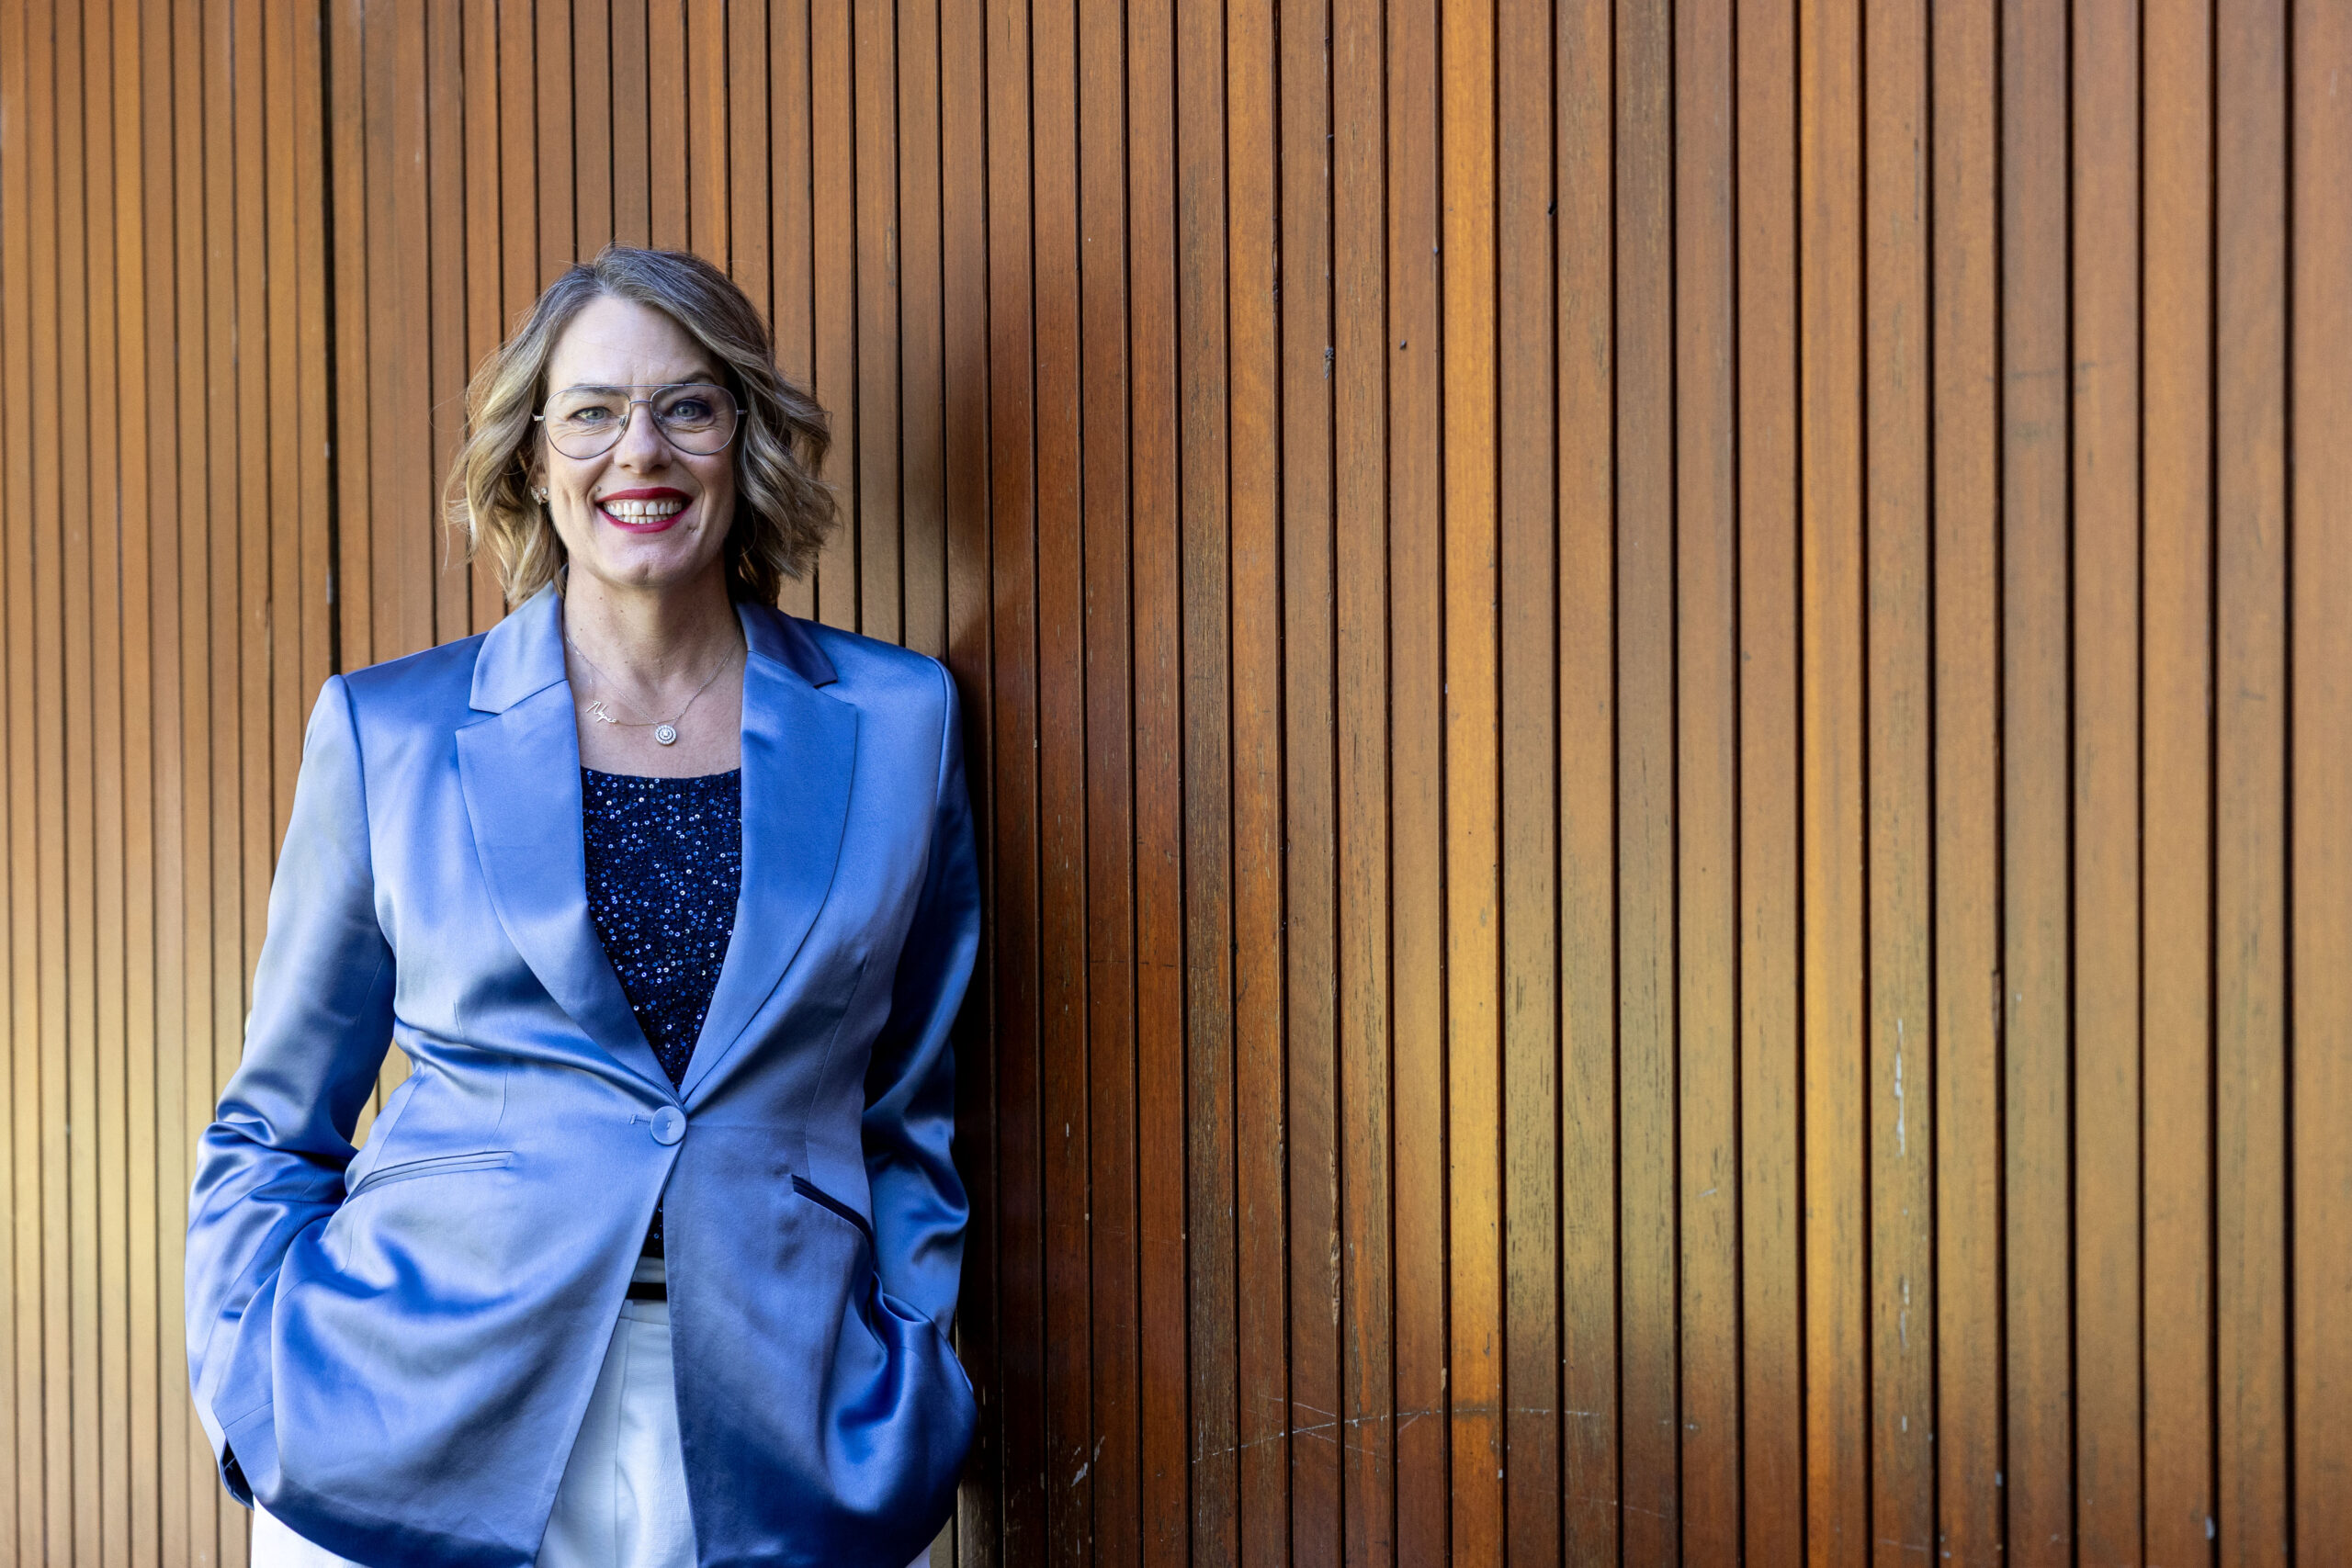
Our founder
Monique Hennessy
Monique founded CL+C on a simple belief: the law should serve your business, not slow it down.
As a business owner herself, she understands the practical decisions that sit behind privacy, data and AI governance. Monique and the CL+C team’s clear advice ensures you’ll always know where you stand, and what comes next.
A team of women lawyers who understand business, inside and out.
Our team
The people you’ll actually work with


Ready to talk it through?
We’ll discuss your matter. There’s no pressure to proceed.
Insights
Plain-English notes & legal insights for business owners



FAQ
Frequently Asked Questions
Questions we’re commonly asked. For advice on your specific matter, request a consultation.
Does the Privacy Act 1988 (Cth) apply to small businesses?
The Privacy Act 1988 (Cth) can apply to a small business, although some small businesses are exempt depending on their circumstances. Factors such as turnover, the nature of the business and the information it handles can affect whether the Act applies. We can help businesses determine their obligations and identify practical gaps in their current privacy practices.
Do we need a privacy policy if we are a small business?
You may need a privacy policy even if your business is small, particularly where the Privacy Act 1988 (Cth) applies or your business collects personal information in ways that require transparency. More importantly, the policy should reflect what your business actually does with information rather than simply being a standard document adopted from elsewhere.
What should we do if personal information is exposed?
What counts as "personal information" under Australian privacy law?
Personal information is any information that identifies you or could reasonably identify a person, and it covers far more than names and addresses. Email addresses, IP addresses, employee performance records and even certain online identifiers can all qualify. Businesses often underestimate how much of their day-to-day data falls into this category, which is usually the first thing worth mapping before anything else.
Do we need an AI policy for our employees?
Are we responsible for data handled by our software providers?
Your business may still have privacy obligations when personal information is handled by a third-party software provider. Using a platform does not necessarily transfer responsibility for how the information is collected, used or disclosed. We can help businesses review vendor arrangements and identify gaps in data handling.
Do we need to review our privacy practices when we introduce new software?
Yes, introducing new software can change how your business collects, stores, accesses or shares personal information and may require your privacy practices to be reviewed. This is particularly relevant where the platform uses AI, transfers information overseas or gives access to third parties.
What's the difference between a privacy breach and a cyber incident?
A cyber incident refers to unauthorised access to your systems, while a privacy breach specifically involves personal information being lost, accessed or disclosed without authorisation. The two often overlap but aren’t identical. A cyber incident that doesn’t involve personal information may not trigger notification obligations, while a privacy breach can occur without any hacking at all, such as an email sent to the wrong recipient. Knowing which one you’re dealing with shapes what you’re legally required to do next.
How often should we review our privacy policies and data practices?
You should review them whenever there is a material change to how your business collects, uses or shares personal information, rather than relying only on an annual review. New software, AI tools, marketing practices, employees or third-party providers can all change your legal position and may require your documentation to be updated.
Can CL+C work with our existing IT, HR or compliance advisers?
Yes, we can work alongside your existing IT, HR, compliance and other professional advisers where appropriate. Privacy, data and AI issues often involve both legal and operational considerations, so coordinating with the people who manage your systems and processes can help ensure the legal advice works in practice.
All services
Explore all our services
A senior lawyer handles your matter with cross-disciplinary expertise, from the first conversation through to resolution.
01
Film, Television & Entertainment
Entertainment law for screen production.
View Service
02
Business & Commercial Law for SMEs
Contracts, disputes and legal risk, sorted.
View Service
03
Privacy, Data & AI Governance
Privacy, data and AI risk, handled.
View Service
04
Employment Law for Employers
Workplace advice for employers.
View Service
05
Intellectual Property & Copyright
Your IP, protected and put to work.
View Service
06
Commercial & Technology Contracts
Contracts that hold up, however they’re tested.
View Service
Contact
Request a consultation
An obligation-free 15-minute conversation about your matter. We’ll explain where you stand and what your next steps could be.
Phone
Office
Level 5, The Brewery, 5 Central Park Avenue, Chippendale.
Working with clients across Greater Sydney and NSW.
Tell us about your situation
Your enquiry is confidential. We won’t add you to mailing lists or share your details.